Every AI decision, on the record.
AI workflows for insurers, audit-ready by construction.
We bring a platform where every AI decision is audit-ready by construction, and build your own workflows on it in weeks. You own the code, the data and the record.
Become a founding design partner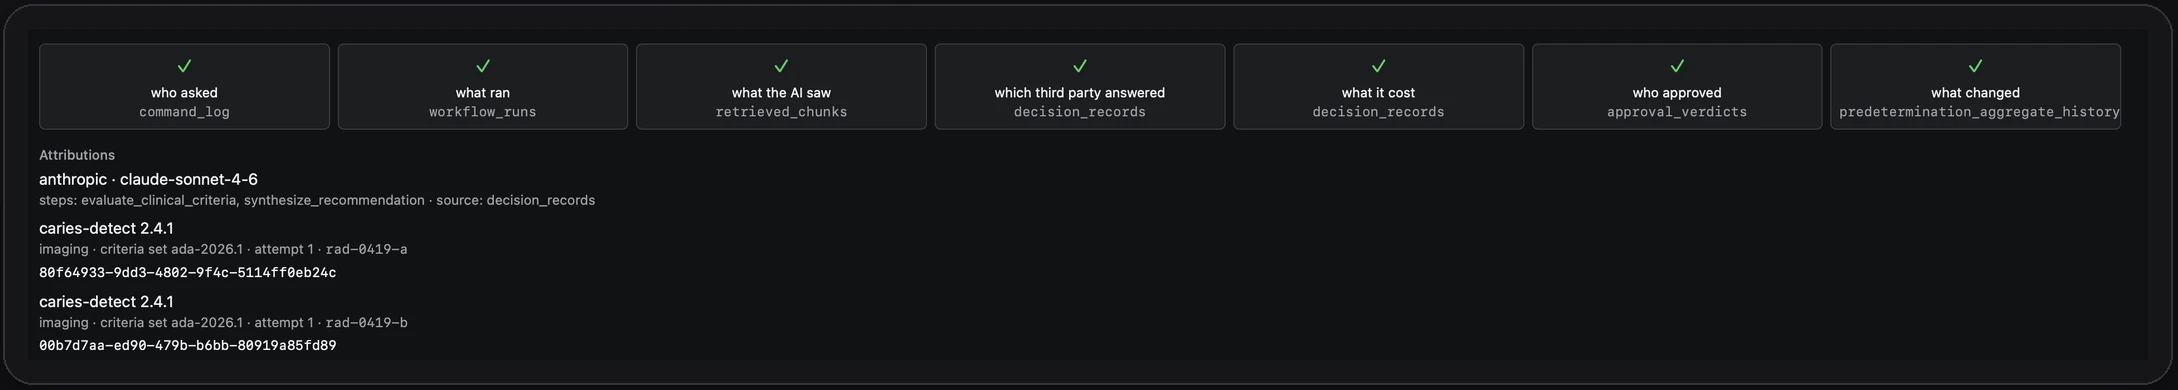
The problem
Insurance AI tends to fail in one of two ways.
Carriers are under pressure to use AI in claims, underwriting and operations. Many projects stall before production, or ship without evidence a regulator will accept.
Nothing ships.
A production AI workflow needs more than a model: authorization, data isolation, protected-data handling, observability, human review, and recovery when a vendor or model fails. Many carriers don't have the AI architects and engineers to build that foundation, so pilots stall.
What ships can't be defended.
Regulators now expect evidence, not policies. Evidence rebuilt from logs after the fact is a legal risk.
And whatever does ship becomes one more system for a small IT team to maintain.
-
25 + D.C.
25 states and D.C. have adopted the NAIC Model Bulletin on insurers' use of AI (as of 31 Aug 2026). California, Colorado, New York and Texas have their own insurance-specific AI regulation or guidance.
Source: NAIC adoption map (opens in a new tab) -
12
states, including Iowa, piloted the NAIC's AI evaluation tool in 2026. It asks insurers for an AI systems inventory, governance-program details, individual model details and data documentation.
Source: Fenwick (opens in a new tab) -
60%
of P&C insurers remain in the exploration or proof-of-concept stage with AI (Capgemini, World Property & Casualty Insurance Report 2026).
Source: Capgemini (opens in a new tab) -
Mar 2026
A federal court ordered UnitedHealth to produce internal documents on how its nH Predict algorithm was designed and implemented, in a proposed class action over AI-assisted Medicare Advantage claim denials. Cigna and Humana have also faced class actions over algorithm-driven claim denials.
Source: Court order (via Georgetown Litigation Tracker) (opens in a new tab)
How it works
Governance built into the architecture, not bolted on.
AI can now write and run software quickly. That makes structure matter more, not less. Gen22 is a platform where the audit trail is part of how the system is built. We build each carrier's workflows on it.
-
01
Code that breaks the trail doesn't ship.
Automated checks run on every push and in CI. They refuse any change that calls an AI model without recording the decision, runs a command or query without declaring its authorization, bypasses the system that records every request, reads or writes data outside approved entry points, or skips tenant data isolation. That holds whether a person or an AI agent wrote the code.
-
02
The carrier owns and runs the whole system.
Code, workflows, data and record, designed to run in the carrier's own environment. Nothing rented.
-
03
One connected record.
Every database row is tied to the request that caused it, the logs and traces around it and, where there is one, the AI decision that produced it and the human approval that confirmed it. Evidence for an examiner is a query, not a project.
-
04
Built for low maintenance.
A live system map, generated from the code, keeps a current inventory of what each system does. Alert thresholds are declared in code, and fired alerts are routed by severity.
What every workflow records today
- Every AI decision: what the model saw, which model and version answered, what it recommended and what it cost.
- A licensed human in charge: workflows pause for review. The model's recommendation and the reviewer's decision are stored separately, so an override is a recorded fact, with notes.
- Third-party vendors: every outside call records the vendor's engine, version and ruleset. Failures and retries stay on record.
- Every permission check, including refusals.
- Health data masked automatically: fields marked as PHI are masked in every log and trace.
- An audit packet on demand, exportable as JSON or PDF. Audit rows are append-only, with retention set per record type.
- Models behind one interface: Anthropic is the provider wired today. Adding another is an adapter, not a rebuild.
Proof
A dental predetermination workflow, built on the platform.
Crown versus alternate benefit, designed so a licensed dental reviewer makes the final call. The model is real. The members, the reviewer and the imaging vendor are synthetic.
No audit code was written for the workflow. The full audit trail came from the platform.
What the test runs produced
A control you have only seen pass is a control you have not seen. So the runs include the failures.
- Three reviewer overrides, each with notes.
- A vendor failure and retry, kept on one record.
- Two real permission refusals. Not staged.
- One request deliberately left pending. The audit packet flags it: who approved ✗
- One unscripted run: the model refused to mark a clinical criterion as met because required evidence was missing, and flagged it for the reviewing dentist.
One view, seven questions
For any request, the audit packet answers seven questions. Each answer is traced to the database table and row it came from.
- Who asked
- What ran
- What the AI saw
- Which third party answered
- What it cost
- Who approved
- What changed
All demo data is synthetic (for example, "Synthetic Member One" and "Dr. Alex Example, DMD"). No real patients, members or carriers were involved. What is built today →
What's next
Where the platform is going.
These are roadmap items, not shipped features. Each one builds on the record the platform already keeps.
Self-maintaining systems
Because the record is complete and connected, AI agents will pick up alerts, follow the record to the cause and propose a fix for a human to approve. The goal: carriers run production AI without hiring an engineering team to maintain it.
Today: alert delivery is built. The agent step is designed, not built.
Workflow templates
Starting points for common insurance work, such as submission intake, rater replacement and bordereaux, so each build starts further ahead.
Using the record before acting
Using the accumulated record as input before a decision is made, not only for audits after the fact.
How we work
One workflow at a time, owned by the carrier.
Built for small and mid-size P&C carriers, MGAs and TPAs, especially teams without a large engineering bench.
-
Step 1
Pick one workflow.
In claims, underwriting or operations. We sit down with your team, and your compliance lead, and agree on a fixed scope.
-
Step 2
We build it on the platform.
Roughly 4–8 weeks, forward-deployed, working alongside the people who will use it.
-
Step 3
You own and run it.
The result is built to run in your own environment. You own the code, the data and the record.
The platform is designed to run in the carrier's own environment. Each engagement also strengthens the platform.
About
Built on one idea: governance belongs in the architecture.
A system that AI can safely operate, extend and repair has to be three things. Legible: its structure is explicit and enforced. Observable: everything it does is recorded and connected. Governed by construction: code that breaks the rules can't ship.
Gen22 is that foundation, starting with insurance, where regulators now ask for evidence of how AI decisions are made.
The name means a new generation of how software is built, starting with the 2022 LLM moment. The mark is a ram's horn.
Gen22 is an early-stage company. The product works today. We have no customers yet and are recruiting founding design partners.
Contact
Become a founding design partner.
Tell us about one AI workflow you'd like to ship and be able to defend. We'll reply to set up a conversation.